Why the DPDP Act Matters for E-commerce and Retail Now
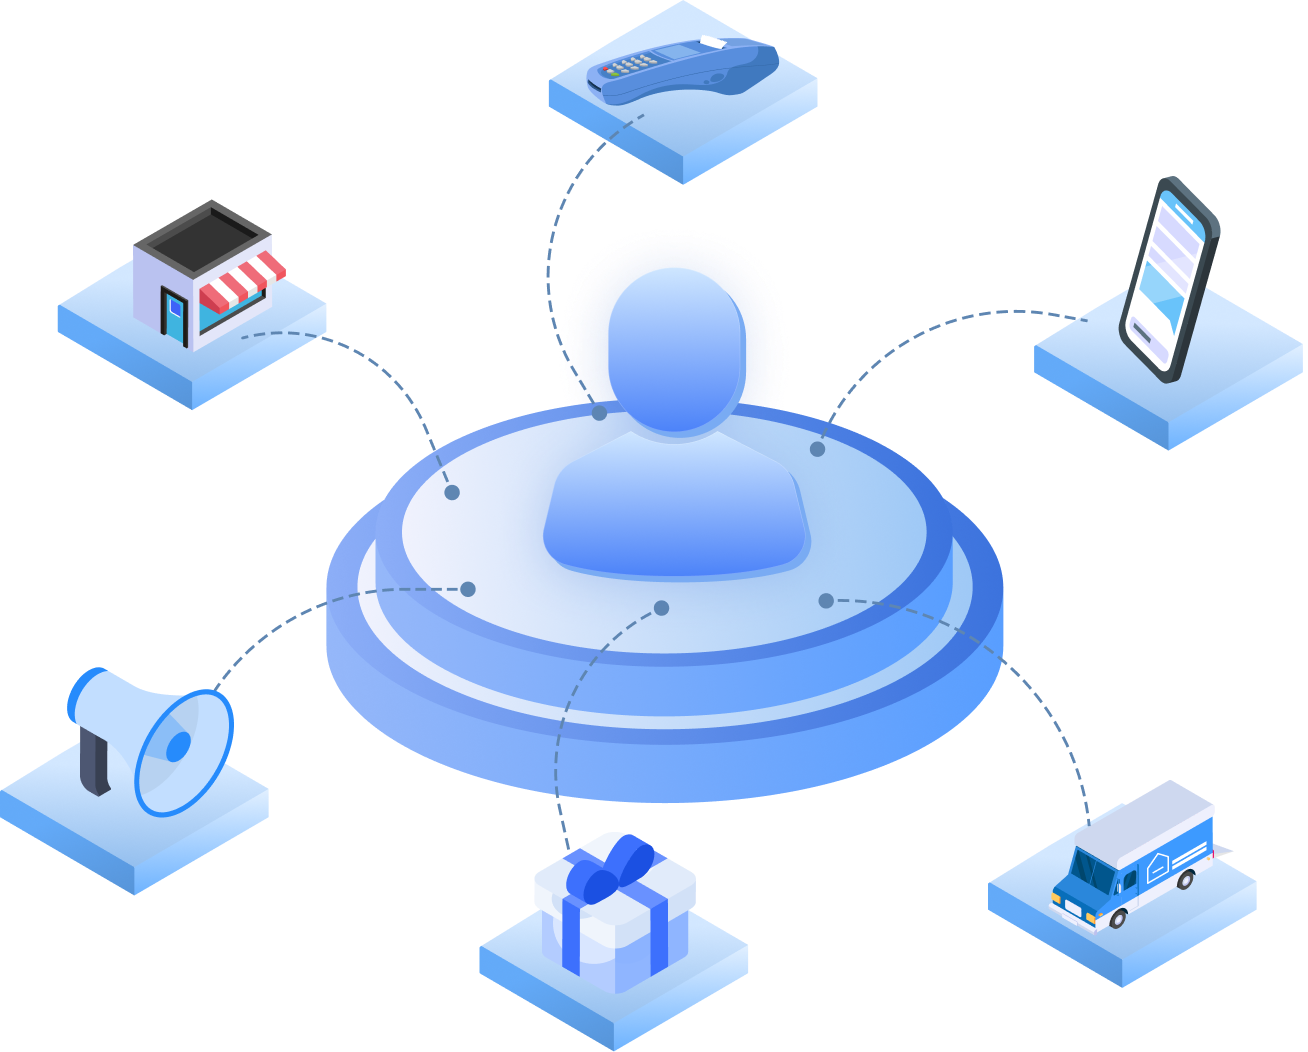
E-commerce platforms and retailers act as Data Fiduciaries, while third-party fulfilment and technology partners often serve as Data Processors. DPDP compliance depends on managing consent across the entire customer lifecycle.

Phased compliance timeline

Cookies become consent infrastructure

Offline data counts

Marketing needs its own consent

Minors shop on your platform

The seller and logistics chain is your liability
Types of Personal Data Processed
Key Compliance & Data Governance Challenges

Customer data is fragmented across storefront, POS, loyalty, CRM, marketing automation, seller dashboards, and 3PL systems.
Cookie and tracking consent is missing or bundled, while the ad stack fires on page load.
POS journeys make phone numbers mandatory for billing, which the Act does not permit for non-essential data.
Loyalty databases built before the Rules lack purpose-specific consent for profiling and marketing.
Identity stitching across store, app, and web into one profile is a separate processing activity nobody captured consent for.
Sellers, franchisees, and logistics partners handle customer data outside the brand's controls.
Built to Solve Every DPDP Challenge
| E-commerce/retail Challenge | Privy by IDfy Capability |
|---|---|
| Customer data scattered across storefront, POS, loyalty, CRM, and 3PL systems | Personal Data Discovery & Governance (Data Compass) maps customer data across every online and offline system |
| Ad and analytics tags firing without valid consent | Cookie Manager brings banner logic, tag behaviour, and preference storage in line with consent requirements |
| Mandatory phone capture at POS | Consent Lifecycle Management enables optional, purpose-specific capture inside POS workflows |
| Legacy loyalty databases without valid consent | Consent remediation campaigns re-engage members and build compliant records before further use |
| Identity stitching without notice | Dedicated consent flows for cross-channel profiling and unified customer profiles |
| Marketing on billing-consent data | Separate transactional and marketing consents, monitored continuously across channels |
| Minors transacting on the platform | Verifiable parental consent workflows built on IDfy's identity verification infrastructure |
| Sellers, franchisees, and 3PLs outside your controls | Continuous Compliance & Risk Management assesses, contracts, and continuously monitors every processor |
| Rights requests spiking during sale seasons | Data Principal Rights Management automates intake, routing, and fulfilment at peak volume |
| No single view of privacy posture across consent, data, and vendor risk | InspectAI gives a unified view across all modules, continuously scanning for gaps |

Customer data scattered across storefront, POS, loyalty, CRM, and 3PL systems
Personal Data Discovery & Governance (Data Compass) maps customer data across every online and offline system
Ad and analytics tags firing without valid consent
Cookie Manager brings banner logic, tag behaviour, and preference storage in line with consent requirements
Mandatory phone capture at POS
Consent Lifecycle Management enables optional, purpose-specific capture inside POS workflows
Legacy loyalty databases without valid consent
Consent remediation campaigns re-engage members and build compliant records before further use
Identity stitching without notice
Dedicated consent flows for cross-channel profiling and unified customer profiles
Marketing on billing-consent data
Separate transactional and marketing consents, monitored continuously across channels
Minors transacting on the platform
Verifiable parental consent workflows built on IDfy's identity verification infrastructure
Sellers, franchisees, and 3PLs outside your controls
Continuous Compliance & Risk Management assesses, contracts, and continuously monitors every processor
Rights requests spiking during sale seasons
Data Principal Rights Management automates intake, routing, and fulfilment at peak volume
No single view of privacy posture across consent, data, and vendor risk
InspectAI gives a unified view across all modules, continuously scanning for gaps
Recommended Implementation Journey

Map the Customer Across Channels
 Discover and classify customer data across storefront, POS, loyalty, CRM, and martech systems.
- Audit what the ad stack actually fires against what the cookie banner claims.
- Scope the loyalty remediation problem: which records lack valid consent for which purposes.
- Inventory sellers, franchisees, 3PLs, and martech vendors; flag agreements missing DPDP terms.


Remediate and Rebuild Consent
- Deploy purpose-specific consent across web, app, POS, and loyalty journeys, with marketing consent separated.
- Run loyalty re-consent campaigns so the database is usable before obligations bite.
- Stand up parental consent flows and rights and breach workflows sized for sale-season volume.
- Close flagged seller, franchise, and 3PL contracts.


Keep Campaigns Provably Consented
- Scan every new campaign, journey, and app release with InspectAI before it introduces consent drift.
- Continuously monitor seller, franchise, and 3PL compliance posture.
- Run DPIAs for new profiling and personalisation programmes if notified as a Significant Data Fiduciary.
- Enforce retention on dormant accounts and stale marketing data.

Key Takeaways

E-commerce platforms and retail brands are Data Fiduciaries under the DPDP Act for customer data collected across web, app, stores, and loyalty programmes; sellers, 3PLs, and martech vendors process it under their direction.

DPDP Rules 2025 were notified on 13 November 2025, with Consent Manager registration from 13 November 2026 and major obligations effective from 13 May 2027.

Consent collected for billing does not cover marketing; promotional messages need separate, explicit, withdrawable consent, and non-essential data cannot be made mandatory for a sale.

Verifiable parental consent applies wherever minors use the platform, and targeted advertising to children is prohibited, with penalties up to ₹250 crore per contravention.

A unified privacy management platform enables faster regulatory responses through cross-channel data mapping, remediated loyalty consent records, automated rights fulfilment at sale-season volume, and continuous seller and 3PL monitoring.

Early DPDP readiness means running loyalty re-consent on your own campaign calendar instead of freezing the database when obligations bite.
Why Privy by IDfy for E-commerce & Retail
Consumer brands trust Privy by IDfy to operationalise DPDP compliance across online and offline channels. Our platform enables consent at every touchpoint, customer data governance across every system, and audit-ready evidence across every partner.
Get every campaign provably consented.
FAQs
In most flows, a platform or brand is a Data Fiduciary, because it decides how customer data is used for sales, personalisation, and marketing. You act as a processor only in narrow flows, such as passing order data to a seller purely for fulfilment. The distinction decides who carries which obligations, so map it per flow.
Notice and consent before non-essential tracking fires, with essential and optional purposes separated and preferences stored as evidence. A banner that loads after the ad stack has already fired is decoration, not compliance. Privy by IDfy's Cookie Manager aligns banner logic, tag behaviour, and records.
Yes. Non-essential personal data cannot be made mandatory for service delivery, so a forced phone capture at checkout risks both the DPDP Act and consumer protection rules. Optional, purpose-specific capture inside the POS journey is the fix.
If members were enrolled without purpose-specific consent for profiling and marketing, yes, before using that data further. A remediation campaign that re-engages members and records itemised consent converts the database from liability back to asset.
Not without separate marketing consent. Consent given for a transaction covers the transaction. Privy by IDfy identifies which records carry valid marketing consent and runs remediation for the rest.


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339