Why the DPDP Act Matters for Fintech Now
Fintechs can act as both Data Fiduciaries and Data Processors under the DPDP Act, depending on whether they control or process personal data. RBI's digital lending rules laid the foundation, while DPDP makes these obligations legally enforceable.

Phased compliance timeline

Consent Manager readiness

RBI already primed this audience

Alternate data sits at the edge

Multi-party chains multiply obligations

Digital-first customers exercise rights
Types of Personal Data Processed
Key Compliance & Data Governance Challenges

Borrower data changes hands between platform, NBFC, and distributor in one transaction, with fiduciary and processor roles rarely mapped per flow.
App permissions collect more than underwriting needs, exactly what RBI's digital lending rules flag and DPDP penalises.
Alternate-data underwriting runs on consent language written before purpose limitation had teeth.
Account Aggregator consent covers the transfer, not everything done with the data after ingestion.
LSP and DSA sourcing chains capture borrower data before the lender's systems ever see it.
Digital-first borrowers file access and erasure requests at volumes manual processes cannot absorb.
Built to Solve Every DPDP Challenge
| Fintech Challenge | Privy by IDfy Capability |
|---|---|
| Fiduciary and processor roles unmapped across platform, NBFC, and distributor | Continuous Compliance & Risk Management maps roles per data flow and manages data-processing agreements centrally |
| App collecting permissions beyond underwriting need | InspectAI scans live digital journeys, flagging collection that exceeds stated purpose |
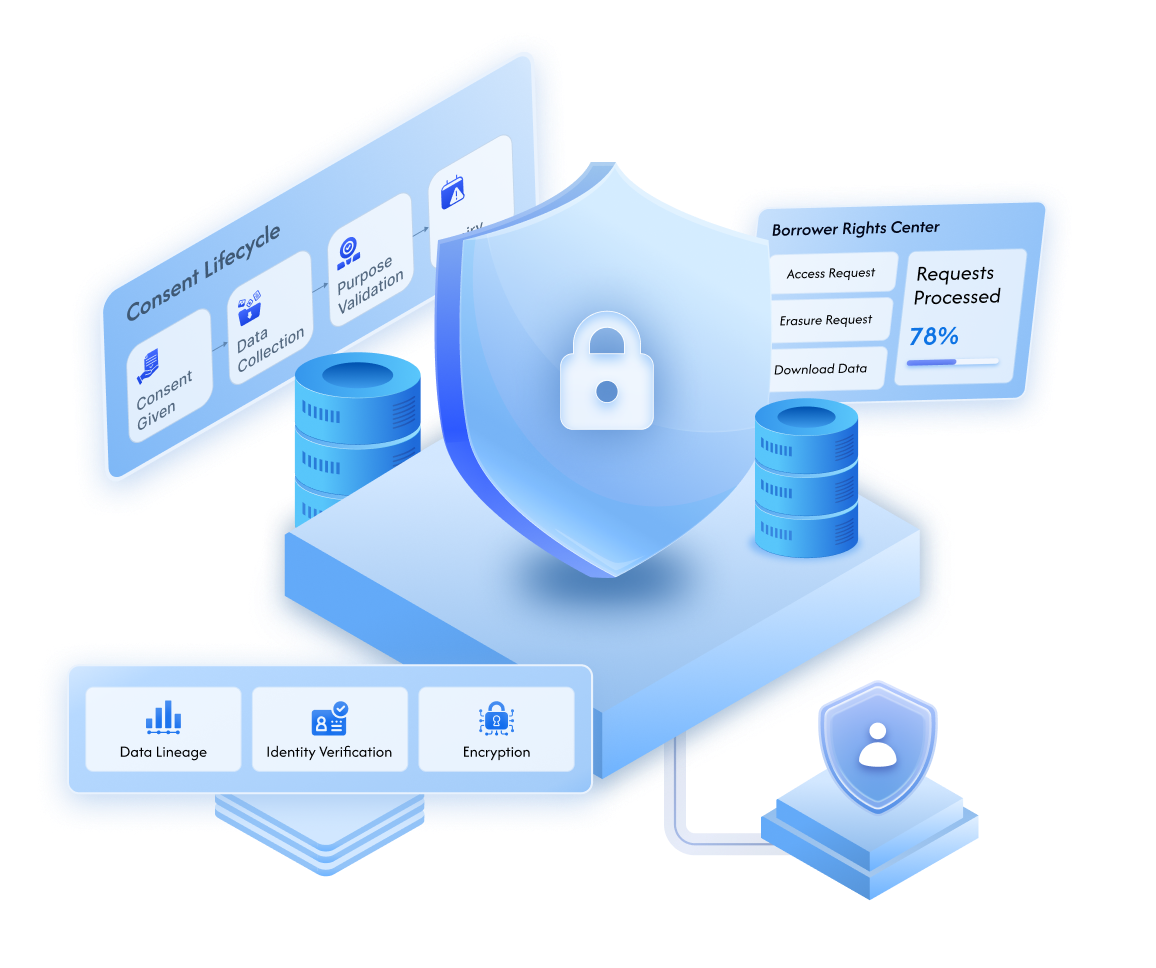
| Alternate-data underwriting on legacy consent language | Consent Lifecycle Management rebuilds purpose-specific, itemised consent and versions every change |
| AA-sourced data losing purpose boundaries after ingestion | Personal Data Discovery & Governance (Data Compass) tags AA-sourced records so purpose limits survive inside your systems |
| LSP and DSA chains collecting data upstream of your controls | Continuous Compliance & Risk Management assesses and continuously monitors every sourcing partner |
| Rights requests arriving through app UI at volume | Data Principal Rights Management automates intake, routing, fulfilment, and audit trails |
| Credit and fraud models needing training data without exposed PII | Data Compass classification enables masking and de-identification ahead of model training |
| Collections conduct creating data liability (recordings, agent access) | Role-based access controls, retention schedules on recordings, and access audit trails |
| Marketing and cross-sell running on transaction-consent data | Separate transactional and marketing consents, monitored continuously across channels |
| No single view of privacy posture across consent, data, and vendor risk | InspectAI gives a unified view across all modules, continuously scanning for gaps |

Fiduciary and processor roles unmapped across platform, NBFC, and distributor
Continuous Compliance & Risk Management maps roles per data flow and manages data-processing agreements centrally
App collecting permissions beyond underwriting need
InspectAI scans live digital journeys, flagging collection that exceeds stated purpose
Alternate-data underwriting on legacy consent language
Consent Lifecycle Management rebuilds purpose-specific, itemised consent and versions every change
AA-sourced data losing purpose boundaries after ingestion
Personal Data Discovery & Governance (Data Compass) tags AA-sourced records so purpose limits survive inside your systems
LSP and DSA chains collecting data upstream of your controls
Continuous Compliance & Risk Management assesses and continuously monitors every sourcing partner
Rights requests arriving through app UI at volume
Data Principal Rights Management automates intake, routing, fulfilment, and audit trails
Credit and fraud models needing training data without exposed PII
Data Compass classification enables masking and de-identification ahead of model training
Collections conduct creating data liability (recordings, agent access)
Role-based access controls, retention schedules on recordings, and access audit trails
Marketing and cross-sell running on transaction-consent data
Separate transactional and marketing consents, monitored continuously across channels
No single view of privacy posture across consent, data, and vendor risk
InspectAI gives a unified view across all modules, continuously scanning for gaps
Recommended Implementation Journey

Map Roles Across Every Lending Flow
 Assign Data Fiduciary or Data Processor roles per flow across platform, lender, and distribution partners.
- Audit app permissions against actual underwriting need, before a supervisory letter does.
- Inventory LSPs, DSAs, and collections partners; flag agreements missing DPDP terms.
- Tag Account Aggregator-sourced data so its purpose boundaries are traceable after ingestion.


Rebuild Consent for Alternate Data
- Deploy itemised, purpose-specific consent for SMS, device, and app-usage data.
- Implement in-app Data Principal rights fulfilment sized for digital-first volumes.
- Establish breach notification workflows and reconcile AA consent artefacts with DPDP records.
- Close flagged partner and collections-agency contracts.


Automate at Product Velocity
- Scan every release with InspectAI so new features and campaigns don't reintroduce permission or consent drift.
- Run DPIAs per new lending product; add algorithmic due diligence for credit models if notified as a Significant Data Fiduciary.
- Appoint an India-based DPO and engage an independent auditor where SDF obligations apply.
- Continuously monitor LSP, DSA, and co-lender compliance posture.

Key Takeaways

A fintech is a Data Fiduciary wherever it decides how and why borrower data is processed, and a Data Processor where it acts on a partner lender's instructions; in embedded finance, both roles can apply within one transaction.

DPDP Rules 2025 were notified on 13 November 2025, with Consent Manager registration from 13 November 2026 and major obligations effective from 13 May 2027.

RBI's digital lending rules already require need-based app data collection with borrower consent; DPDP layers purpose limitation, Data Principal rights, and penalties up to ₹250 crore on top.

Account Aggregator consent governs the transfer of financial data; DPDP governs everything done with it after ingestion. The frameworks stack rather than substitute.

A unified privacy management platform enables faster regulatory responses through per-flow role mapping, versioned consent records, automated in-app rights fulfilment, and continuous partner monitoring.

Early DPDP readiness lets lending teams fix app permissions and legacy consent language on their own release schedule instead of under an RBI or Board inquiry.
Why Privy by IDfy for Fintech
Digital lenders and financial services groups trust Privy by IDfy to operationalise DPDP compliance across multi-party lending chains. Our platform enables consent governance at product velocity, borrower data protection at the record level, and audit-ready evidence at startup speed.
Get your lending stack audit-ready
FAQs
Usually both, for their respective purposes. The platform decides how data is used for distribution and experience; the lender decides how it is used for credit. Each carries fiduciary obligations independently, which is why role mapping per flow matters more than a single label for the company.
The Account Aggregator framework lets customers consent to sharing financial data between regulated entities, under the RBI. The DPDP Consent Manager is a registered intermediary for managing consent across platforms generally, under the Data Protection Board, with registration opening on 13 November 2026. Structurally similar, broader in scope, different regulator.
The AA consent artefact governs the transfer. Once data enters your systems, DPDP's purpose limitation, retention, and rights obligations govern its use. Treating the AA artefact as blanket DPDP consent is one of the most common gaps in lending stacks today.
Only with specific consent, informed, and itemised for that purpose, and only where collection is need-based, which RBI's digital lending rules already require. Broad "improve our services" language does not survive DPDP's validity tests.
Yes. They capture borrower data on your behalf before your systems see it, which makes their conduct your accountability as a fiduciary. Assessment, contracts, and continuous monitoring are the control set.
No. Bureau reporting is mandated under the Credit Information Companies (Regulation) Act, 2005, making it a legitimate use under Section 7 of the DPDP Act. Notice is required; a consent checkbox you cannot honour on withdrawal creates risk rather than compliance.


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339