Why the DPDP Act Matters for Insurance Now
Under the DPDP Act, insurers are Data Fiduciaries, while TPAs, hospitals, brokers, and other partners act as Data Processors. Effective compliance begins with mapping these data flows.

Phased compliance timeline

Consent Manager readiness

DPDP and IRDAI alignment

Health data in every file

Third-party accountability

Governance before compliance
Types of Personal Data Processed
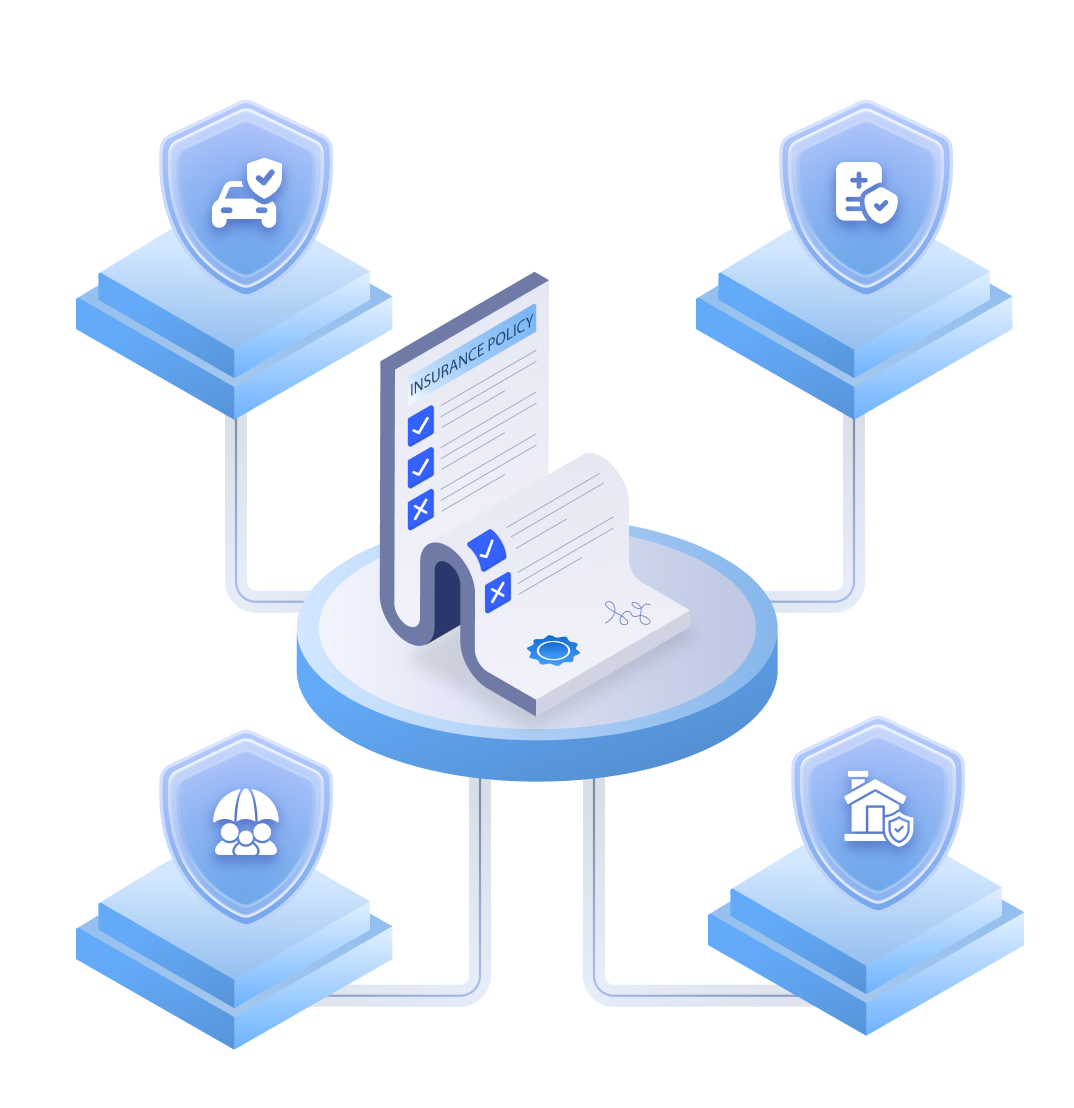
Key Compliance & Data Governance Challenges

Policyholder data is fragmented across policy administration, claims, underwriting, distribution, and grievance systems.
Consent is captured differently across agents, bancassurance partners, web aggregators, branches, and apps.
Claims processing routes health data through hospitals, TPAs, and surveyors, multiplying the processor risk surface.
Nominee and dependent data enters systems without the nominee ever seeing a notice.
Medical underwriting data retention often has no defined endpoint, decades after policies lapse.
Larger insurers are likely Significant Data Fiduciary candidates, bringing DPIA and audit obligations once notified.
Built to Solve Every DPDP Challenge
| Insurance Challenge | Privy by IDfy Capability |
|---|---|
| Health, financial, and nominee data scattered across policy admin, claims, and TPA systems | Personal Data Discovery & Governance (Data Compass) maps personal data across structured and unstructured systems, including scanned proposal forms and medical reports |
| Consent captured inconsistently across agents, bancassurance, aggregators, and apps | Consent Lifecycle Management unifies capture, versioning, and withdrawal across every distribution channel |
| Claims data flowing through hospitals, TPAs, and surveyors without monitored agreements | Continuous Compliance & Risk Management monitors every processor against data-processing agreement terms |
| Nominee and dependent data processed without notice | Consent Governance supports multi-party notice and consent flows for nominees and family floater members |
| No retention endpoint on underwriting and lapsed-policy archives | Data Compass tags each record's retention basis and automates deletion where no mandate applies |
| Policyholder rights requests spanning policy admin, claims, and TPA systems | Data Principal Rights Management routes and fulfils access, correction, and erasure requests across connected systems |
| Breach response spanning insurer and TPA systems within statutory windows | Continuous Compliance & Risk Management provides an auditable, time-stamped incident workflow covering DPDP and IRDAI reporting |
| Anticipated Significant Data Fiduciary obligations (DPIA, India-based DPO, audits) | Continuous Compliance & Risk Management runs the DPIA cycle and builds the evidence trail regulators expect |
| Wellness apps and portals using tracking cookies without DPDP-aligned consent | Cookie Manager brings banner logic and preference storage in line with consent requirements |
| No single view of privacy posture across consent, data, and vendor risk | InspectAI gives a unified view across all modules, continuously scanning for gaps |

Health, financial, and nominee data scattered across policy admin, claims, and TPA systems
Personal Data Discovery & Governance (Data Compass) maps personal data across structured and unstructured systems, including scanned proposal forms and medical reports
Consent captured inconsistently across agents, bancassurance, aggregators, and apps
Consent Lifecycle Management unifies capture, versioning, and withdrawal across every distribution channel
Claims data flowing through hospitals, TPAs, and surveyors without monitored agreements
Continuous Compliance & Risk Management monitors every processor against data-processing agreement terms
Nominee and dependent data processed without notice
Consent Governance supports multi-party notice and consent flows for nominees and family floater members
No retention endpoint on underwriting and lapsed-policy archives
Data Compass tags each record's retention basis and automates deletion where no mandate applies
Policyholder rights requests spanning policy admin, claims, and TPA systems
Data Principal Rights Management routes and fulfils access, correction, and erasure requests across connected systems
Breach response spanning insurer and TPA systems within statutory windows
Continuous Compliance & Risk Management provides an auditable, time-stamped incident workflow covering DPDP and IRDAI reporting
Anticipated Significant Data Fiduciary obligations (DPIA, India-based DPO, audits)
Continuous Compliance & Risk Management runs the DPIA cycle and builds the evidence trail regulators expect
Wellness apps and portals using tracking cookies without DPDP-aligned consent
Cookie Manager brings banner logic and preference storage in line with consent requirements
No single view of privacy posture across consent, data, and vendor risk
InspectAI gives a unified view across all modules, continuously scanning for gaps
Recommended Implementation Journey

Map the Policy and Claims Estate
 Discover and classify policyholder data across policy admin, claims, and underwriting, including scanned proposal forms and medical reports.
- Audit consent capture across agents, bancassurance, aggregators, and direct channels.
- Inventory every TPA, hospital empanelment, surveyor, and broker touching policyholder data.
- Flag processor agreements missing DPDP-grade purpose, scope, and retention terms.


Rebuild Consent Across Distribution
- Deploy purpose-specific consent at proposal stage, including nominee notice flows.
- Implement policyholder rights workflows spanning insurer and TPA systems.
- Establish breach notification covering both Data Protection Board and IRDAI reporting.
- Renegotiate TPA, hospital, and surveyor contracts flagged in the audit.


Govern the Claims Chain Continuously
- Run DPIAs for each new product line; health and telematics products trigger them fastest.
- Appoint an India-based DPO and engage an independent data auditor if notified as a Significant Data Fiduciary.
- Enforce retention schedules on lapsed-policy and underwriting archives.
- Continuously monitor TPA and hospital compliance posture through the platform.

Key Takeaways

Insurers are Data Fiduciaries under the DPDP Act for proposal, medical, claims, and nominee data; TPAs, hospitals, and surveyors process it as Data Processors under their direction.

DPDP Rules 2025 were notified on 13 November 2025, with Consent Manager registration from 13 November 2026 and major obligations effective from 13 May 2027.

Non-compliance can attract penalties of up to ₹250 crore per contravention, and the harm profile of health and claims data will weigh in penalty decisions.

IRDAI requirements on cyber security, outsourcing, and policyholder protection apply alongside DPDP, requiring insurers to manage both frameworks together.

A unified privacy management platform enables faster regulatory responses through centralised data mapping across the claims chain, nominee-aware consent records, automated rights management, and continuous TPA monitoring.

Early DPDP readiness lets insurers remediate decades of legacy underwriting archives on their own schedule instead of under a Board inquiry.
Why Privy by IDfy for Insurers
Leading insurers and financial services groups trust Privy by IDfy to operationalise DPDP compliance across health-data-heavy ecosystems. Our platform enables continuous data governance, centralised consent management, and audit-ready compliance at enterprise scale.
Get your claims chain audit-ready
FAQs
An insurer is a Data Fiduciary for the policyholder data it collects, because it determines the purpose and means of processing across underwriting, servicing, and claims: TPAs, surveyors, and BPOs processing that data on its behalf act as Data Processors under contract.
Yes. Under the DPDP Act, the Data Fiduciary remains accountable for processing done on its behalf. A TPA retaining claims files beyond their purpose, or a hospital sharing discharge data without controls, lands on the insurer, which is why processor agreements and continuous monitoring matter more here than in most sectors.
No. Unlike GDPR, the DPDP Act does not define a separate sensitive-data tier. All personal data carries the same statutory obligations, but medical and claims data raise the practical stakes: the harm from a breach is higher, and regulators will weigh that in penalty decisions.
Data Principals can access, correct, and erase their personal data, nominate someone to exercise rights on their behalf, and raise grievances. These sit alongside the rights of policyholders under IRDAI's protection regulations; the two frameworks stack.
The nominee is a Data Principal in their own right. When a policyholder submits nominee details, the insurer processes a third party's personal data, so notice obligations apply to the nominee, and consent architecture should account for them rather than treating nominee fields as the policyholder's data.
Paper consent letters digitised into policy files rarely meet DPDP standards: consent must be specific, informed, and itemised per purpose, with a withdrawal path as easy as the grant. Privy by IDfy replaces letter-format consent with purpose-specific digital records that survive an audit.


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339