Aadhaar Verification and Masking
Definition
Verifying identity using Aadhaar while masking sensitive digits to protect personal data.
Aadhaar verification and masking refer to the process of validating an individual’s identity using Aadhaar while ensuring that the full number is not exposed or stored unnecessarily. Masking limits the visibility of sensitive digits, typically showing only partial information, reducing the risk of misuse while still enabling identity verification.
In India, Aadhaar is widely used for identity validation across financial services, telecom, and digital platforms. However, its use is tightly regulated, requiring organizations to minimize data exposure and avoid storing full identifiers unless necessary. In the context of the Digital Personal Data Protection Act, 2023, this aligns with principles of data minimization and purpose limitation, ensuring that personal data is only used to the extent required.
In practice, gaps emerge when:
- Full Aadhaar numbers are stored or displayed beyond verification needs.
- Masking is applied inconsistently across systems and workflows.
- Verification processes do not clearly separate identity validation from data storage.
- There is limited visibility into where Aadhaar data is accessed or used.
To address this, organizations design verification flows that validate identity without exposing or retaining sensitive identifiers. This includes enforcing masking by default, limiting storage, and ensuring that access to Aadhaar data is controlled and traceable. Within Privy, this is supported through identity verification workflows, consent linkage, and audit trails, enabling organizations to use Aadhaar for verification while maintaining strong privacy controls.
Questions About Staying in Control?
Here’s everything you need to know about this term and how it fits into your compliance program.
Because Aadhaar is a sensitive personal identifier, and exposing the full number increases the risk of misuse or identity theft.
Only where explicitly permitted and necessary. In most cases, masking and minimal retention are expected to reduce risk.
When full identifiers are logged, shared, or stored across systems without proper controls or masking.
Limiting data exposure, enforcing masking, controlling access, and ensuring usage aligns with defined purposes.
Masking reduces visible exposure of data, while encryption protects data at rest or in transit. Both serve different purposes.
Still have a question?
Latest Blog
Nov 09, 2026
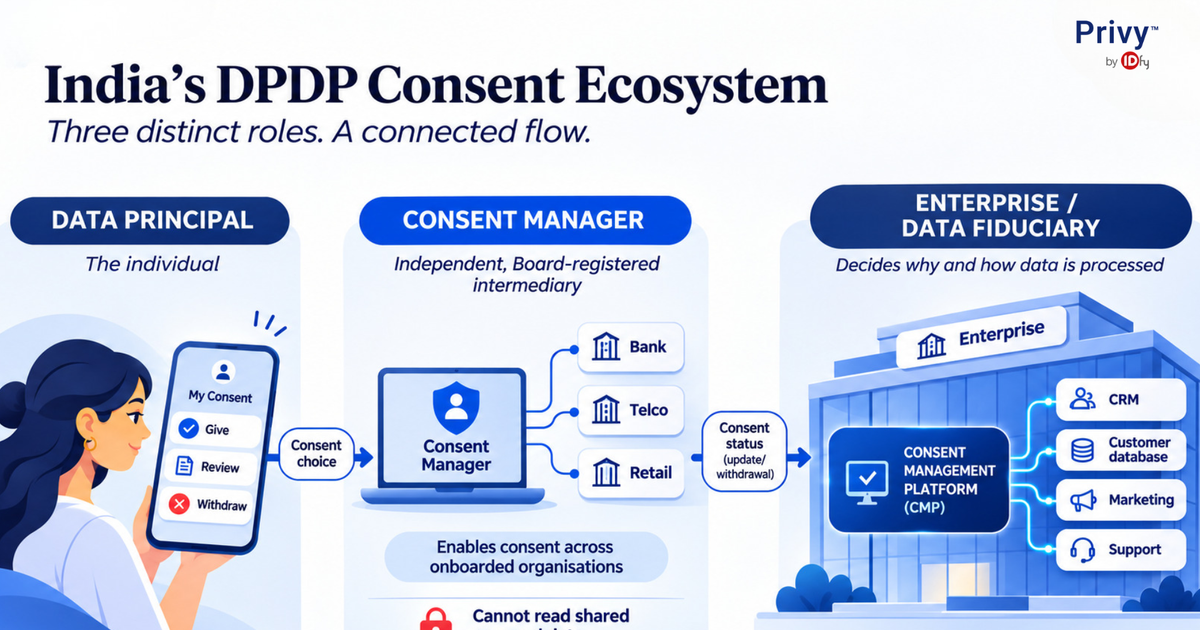
Consent Manager vs Consent Management Platform: What 13 November Changes for Indian Enterprises
Nov 05, 2026
Unstructured Data and DPDP: Where Personal Data Hides in Email, Chat, and Call Recordings
Nov 03, 2026


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339