Data Subject Access Request (DSAR)
Definition
A Data Subject Access Request (DSAR) is a request made by an individual under certain privacy laws, such as the GDPR, to access information about how their personal data is being processed.
DSAR stands for Data Subject Access Request. It is a formal request in which an individual asks an organisation to confirm whether it holds their personal data, and to give them access to it and to details of how it is used. The term comes from the GDPR. India’s DPDP Act does not use it, but it gives Data Principals comparable rights.
Under the GDPR, the individual is called a data subject and the right of access is set out in Article 15. A DSAR can ask for:
confirmation that the organisation is processing their personal data
a copy of that data
the purposes of the processing and the categories of data involved
who the data has been shared with
how long it will be kept, and where it came from
information about their rights to correct, erase or complain
Organisations normally verify the requester’s identity before responding. Under the GDPR, the reply is due within one month, which can be extended by up to two further months for complex requests, and the first copy is free.
How a DSAR is handled
Receive and log the request.
Verify the requester’s identity.
Find the personal data across systems, vendors, and archives.
Review the data and remove information about other people.
Respond within the deadline.
Keep a record of what was requested and what was sent.
DSAR vs DPDP Data Principal rights
The DPDP Act, 2023 does not use the term DSAR. It gives Data Principals four rights: access to information about their personal data (Section 11), correction, completion, updating and erasure (Section 12), grievance redressal (Section 13) and nomination (Section 14).
The right of access is framed differently from a GDPR DSAR. Under Section 11, a Data Principal can obtain, from a Data Fiduciary it has previously given consent to, a summary of the personal data being processed and the processing activities, plus the identities of the other Data Fiduciaries and Data Processors the data has been shared with, along with a description of what was shared. It is built around a summary and the sharing, not a copy of the data itself.
These DPDP rights apply from 13 May 2027. Under Rule 14 of the DPDP Rules, 2025, Data Fiduciaries must publish how Data Principals can exercise them.
If you operate in both India and the EU, treat the two as different obligations. One workflow can handle both, but the checklist, the content of the reply and the deadlines differ. For more on how requests work in India, read What Is a DSR? Data Subject Requests Under India’s DPDP Act.
What organisations need in place
Responding accurately and on time depends on knowing where personal data lives. That means a current data inventory, documented processing activities, a consistent identity verification step, and a workflow that tracks every request to closure.
In practice, gaps emerge when:
Organisations confuse GDPR DSAR obligations with DPDP requirements.
Personal data is spread across multiple systems, which delays responses.
Identity verification is inconsistent before personal data is released.
Privacy teams collect information manually from different applications.
Request handling differs across countries without documented governance.
Organisations improve request management by maintaining accurate data inventories, using workflow automation and standardising identity verification.
How Privy helps
Privy supports request management through data discovery, data mapping, request workflows, consent management and audit-ready reporting, so teams can find personal data across systems and respond to privacy requests under DPDP and other regimes. Its Data Principal Rights Management (DPRM) module brings requests, owners, and deadlines into one workflow.
Questions About Staying in Control?
Here’s everything you need to know about this term and how it fits into your compliance program.
A Data Subject Access Request (DSAR) is a request made by an individual under laws such as the GDPR to access information about how an organization processes their personal data.
No. The DPDP Act does not use the term DSAR. Instead, it provides rights to Data Principals, including the right to obtain information, correction, erasure where applicable, grievance redressal, and nomination.
A DSAR is based on GDPR terminology, whereas the DPDP Act uses the concept of Data Principal Rights. While both relate to individual privacy rights, the legal rights and terminology are not identical.
Organizations subject to GDPR or similar privacy laws may receive DSARs from individuals whose personal data they process.
Privy supports organizations through data discovery, request management workflows, consent management, governance automation, and audit-ready reporting to improve privacy operations across multiple regulatory frameworks.
Still have a question?
Latest Blog
Oct 19, 2026
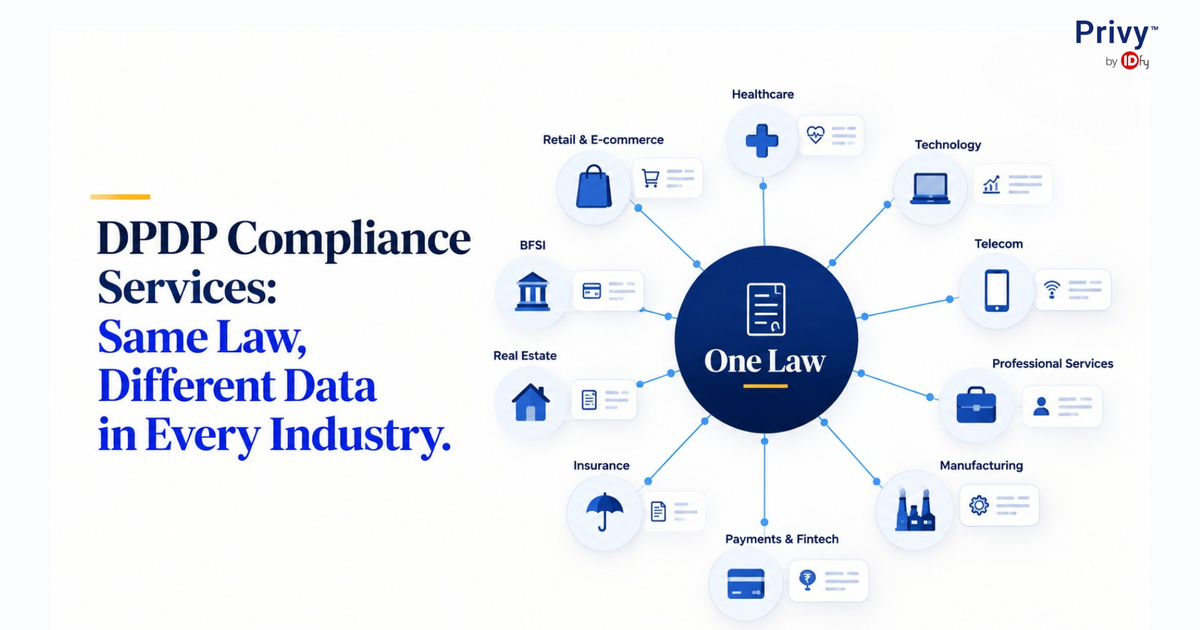
DPDP Compliance Services: Same Law, Different Data in Every Industry
Sep 30, 2026
RBI NBFC Rules Just Banned Dark Patterns and Fake Consent
Sep 29, 2026


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339