Third-party Data Processing
Definition
Third-party data processing refers to situations where a Data Fiduciary engages another entity to process personal data on its behalf under the DPDP Act.
Under the DPDP Act, third-party data processing refers to the processing of personal data by an external entity, such as a Data Processor, on behalf of a Data Fiduciary.
Organizations often rely on third parties for services such as cloud infrastructure, customer support, analytics, identity verification, and technology platforms. When these third parties process personal data, the Data Fiduciary remains responsible for ensuring that processing is carried out in accordance with DPDP obligations.
Effective third-party data processing management requires organizations to understand what personal data is shared, why it is shared, who processes it, what safeguards are implemented, and how third-party relationships are governed.
Organizations need appropriate contracts, security requirements, monitoring processes, and oversight mechanisms to manage risks associated with external data processing activities.
In practice, gaps emerge when:
- Organizations do not have visibility into all third parties handling personal data.
- Data sharing purposes are unclear.
- Third-party security practices are not evaluated.
- Data Processor activities are not monitored.
- Personal data continues to be shared after the purpose ends.
Organizations address these challenges by maintaining vendor inventories, conducting third-party risk assessments, defining processing responsibilities, monitoring Data Processors, and maintaining documentation. Within Privy, capabilities such as data mapping, vendor risk workflows, consent management, and compliance reporting help organizations manage third-party data processing.
Questions About Staying in Control?
Here’s everything you need to know about this term and how it fits into your compliance program.
It refers to situations where an external entity processes personal data on behalf of a Data Fiduciary.
The Data Fiduciary remains responsible for ensuring compliance with DPDP obligations while engaging Data Processors.
It helps organizations maintain control over personal data shared with external entities and reduce privacy risks.
Organizations should monitor data shared, processing purposes, security safeguards, and compliance responsibilities.
Privy helps organizations gain visibility into data flows, manage privacy workflows, and track governance activities involving third parties.
Still have a question?
Latest Blog
Sep 30, 2026
RBI NBFC Rules Just Banned Dark Patterns and Fake Consent
Sep 29, 2026
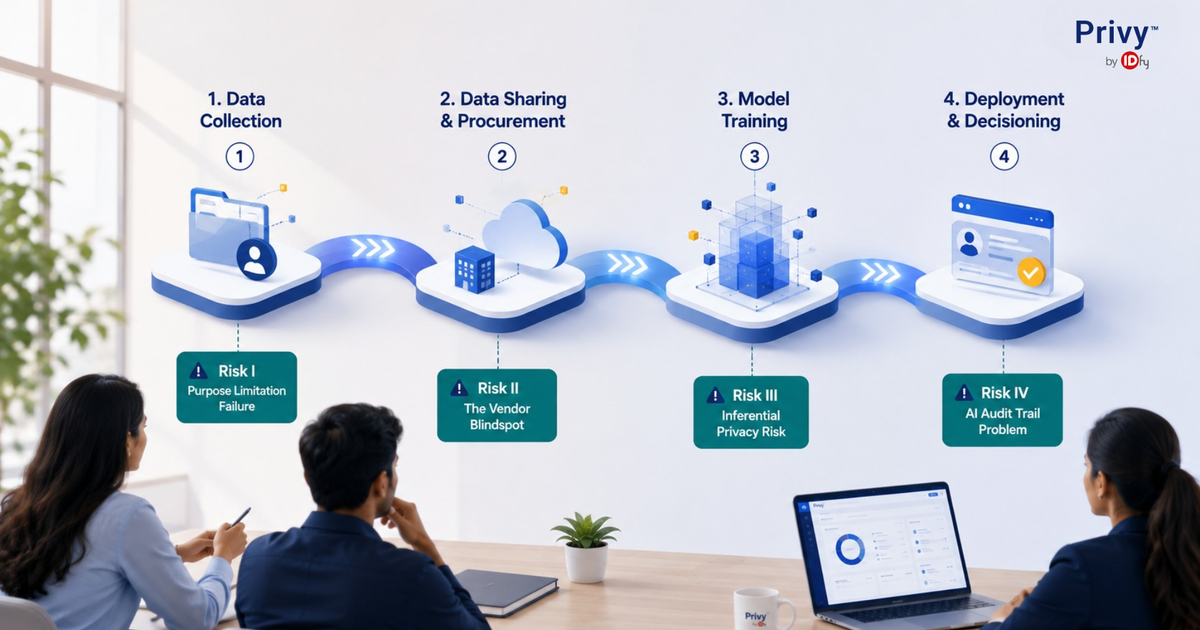
Data Privacy in the AI Era: The Four Risks Indian Corporations Have Already Inherited
Sep 10, 2026


 shivani@idfy.com
 Unit no. 801, Skyline Icon, 804, Andheri - Kurla Rd, Chimatpada, Marol, Andheri East, Mumbai, Maharashtra 400059
 1800 123 4339